Spotting phishing: five typical tricks
AI-generated emails are flawless and personal — the old tell-tale signs no longer apply. These five patterns every team should know.
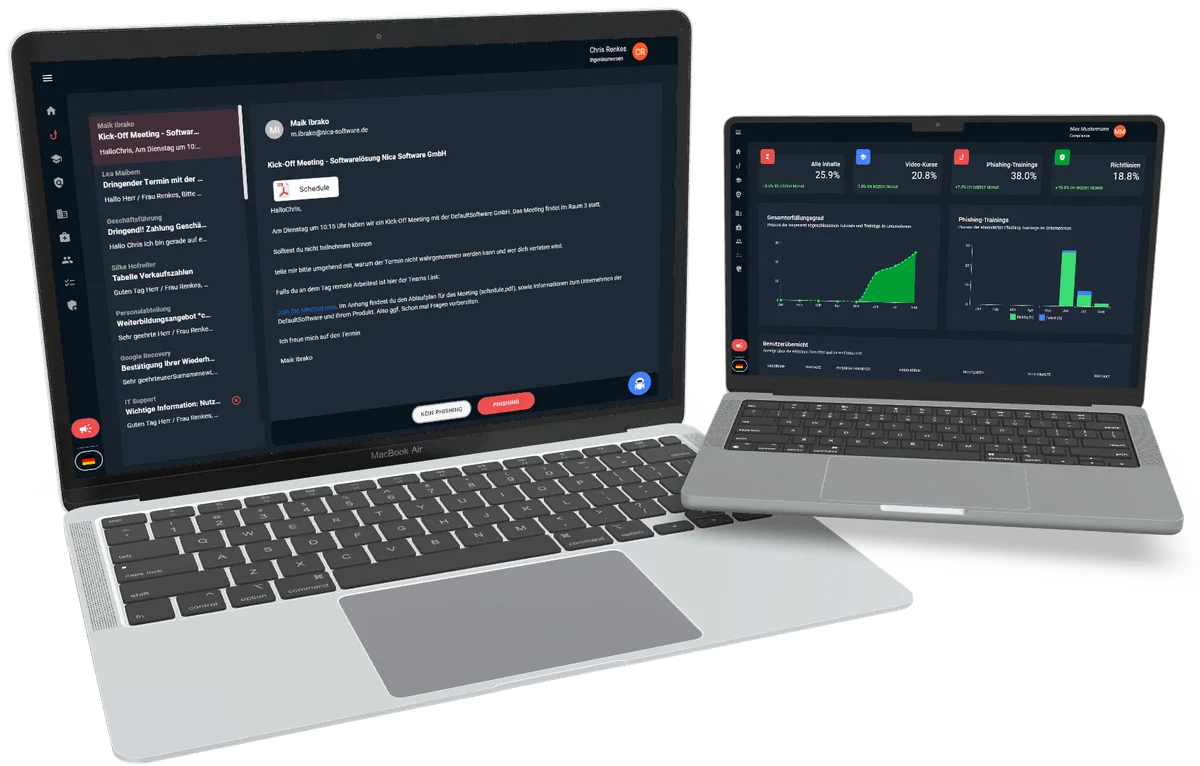
“Watch out for spelling mistakes” — that advice is obsolete. Modern phishing emails are flawless, personally addressed and imitate real senders convincingly. Instead of hunting for typos, it pays to know the scams behind them: online fraud keeps repeating the same five patterns.
- Artificial time pressure — a deadline that pushes for immediate action.
- CEO fraud — a supposedly confidential request from the top.
- The almost-correct sender address.
- The unexpected attachment that urges you to open it.
- The QR code whose destination is hard to check.
1. Artificial time pressure
“Your account will be locked in 24 hours.” Pressure switches off critical thinking. Reputable senders rarely set such tight, threatening deadlines.
2. The boss who discreetly asks for something
CEO fraud plays on hierarchy and secrecy. A supposed request from management for a “confidential, short-term” transfer should always be verified via a second channel.
The most effective defence isn't a filter but a team that reports suspicious emails instead of clicking them.
3. The almost-right address
The real domain is often not at the end of the sender address. “microsoft.com.security-alert.io” is not Microsoft. A glance at the actual domain part exposes many fakes.
4. The attachment that pushes
Unexpected invoices, parcel notifications or “voice messages” as attachments are among the typical entry points. When in doubt: don't open — report.
5. The QR code
Quishing shifts the attack to the smartphone, where the URL is harder to check. A QR code in an email deserves the same scepticism as a link.
The goal of awareness isn't to stop everyone from ever clicking — that's unrealistic. The goal is a culture where reporting is natural and a wrong click becomes a learning unit, not a penalty.
Related from our offering
Keep reading
 AI-generated image
BCM software: business continuity management with NICA BCM — aligned with BSI Standard 200-4 and ISO 22301
Business continuity management has not been a side issue since 2020 at the latest. Anyone who wants to stay able to act in an emergency needs a clear framework — and the right tools. This article explains why structured emergency preparedness is necessary, which standards set the framework and how NICA BCM supports companies in putting it into practice.
 AI-generated image
Business continuity management (BCM): a guide for resilient organisations
According to the Allianz Risk Barometer 2026, business interruption is one of the three biggest business risks worldwide — and it hits companies of every size. Whether cyberattacks, natural disasters or supply chain problems: without a plan, operations, reputation and customer relationships are at stake in an emergency. This guide explains how business continuity management works as a systematic approach, what regulations such as NIS2, DORA and the German KRITIS umbrella act require, and how to build an effective business continuity management system pragmatically.